Objects : Objects > Applications : Applications Overview

Applications Overview
The Applications page lists various attributes of each application definition, such as the application’s relative security risk (1 to 5). The risk value is based on criteria such as whether the application can share files, is prone to misuse, or tries to evade firewalls. Higher values indicate higher risk.
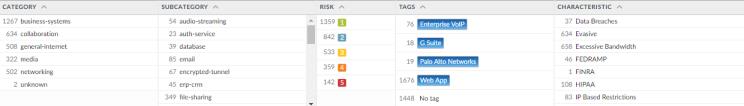
The top application browser area of the page lists the attributes that you can use to filter the display as follows. The number to the left of each entry represents the total number of applications with that attribute.
Note: 
*
The following table describes application details—custom applications and Palo Alto® Networks applications might display some or all of these fields.
•
•
To customize this setting, click the Customize link, enter a value (1-5), and click OK.
Edit Tags to add or remove tags for an application.
To customize this setting, click the Customize link, enter a value, and click OK.
Indicates whether the App-ID is enabled or disabled. If an App-ID is disabled, traffic for that application will be treated as the Previously Identified As App-ID in both Security policy and in logs. For applications added after content release version 490, you have the ability to disable them while you review the policy impact of the new app. After reviewing policy, you may choose to enable the App-ID. You also have the ability to disable an application that you have previously enabled. On a multi-vsys firewall, you can disable App-IDs separately in each virtual system.
When the firewall is not able to identify an application using the App-ID, the traffic is classified as unknown: unknown-tcp or unknown-udp. This behavior applies to all unknown applications except those that fully emulate HTTP. For more information, refer to Monitor > Botnet.
You can create new definitions for unknown applications and then define security policies for the new application definitions. In addition, applications that require the same security settings can be combined into application groups to simplify the creation of security policies.
Objects > Applications